Voice Agent Deployment Lab
The layer between a voice agent and a business action: who's calling, what they're allowed to do, and whether it already happened.
Built as proof-of-work. Not affiliated with Bland.
- Status
- Independent prototype · public demo
- Stack
- Next.js · TypeScript · Postgres (Neon)
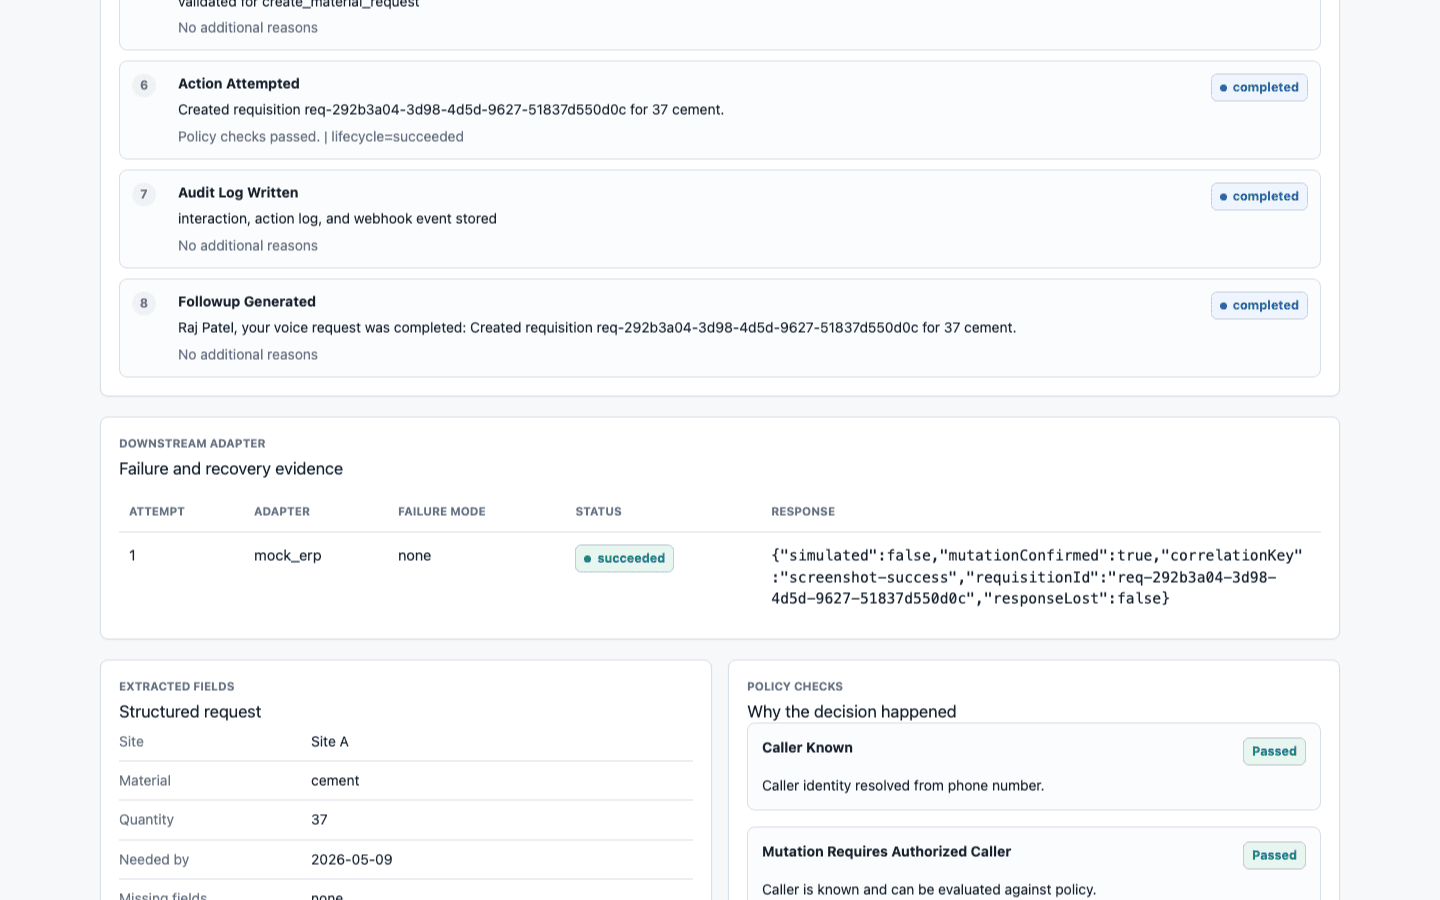
Called for real through Bland's Custom API; an identical replay returned the same requisition instead of a duplicate.
Layman's Version
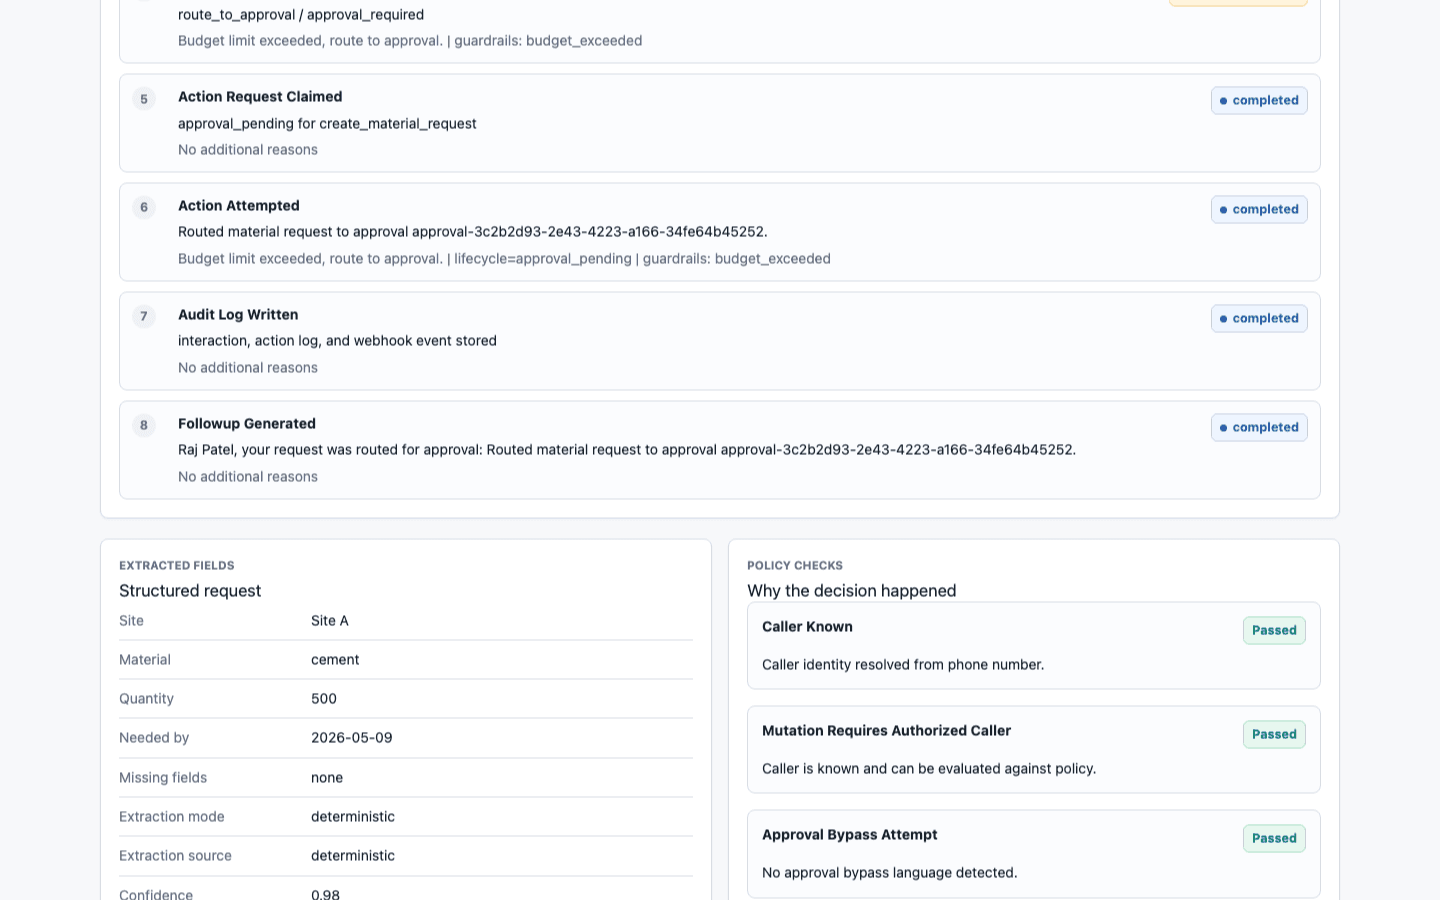
A phone agent can understand 'order 37 bags of cement for Site A', but understanding isn't permission. Someone has to check who's calling, whether they're allowed to order that, whether the order already went in, and keep a record.
This lab is that layer. It isn't a voice model. It takes what the agent extracted and decides whether it becomes a real action, needs a person's approval, or gets refused.
Technical Version
One path for every action
- transcript
- extraction
- caller
- policy
- action
- audit
A single action gateway is used by the simulator, the demo, the webhook, the evals and trace verification. Extraction is deterministic by default; optional LLM extraction is validated and can't authorize anything.
Verification
npm run eval reports 50/50 with 0 unsafe actions. That's a deterministic regression over scripted scenarios: it shows the policy engine behaves as specified, not that a model or a live deployment is reliable.
The hardened version was also called for real through Bland's Custom API against a temporary deployment with an authenticated webhook. It created a requisition in Neon, and an identical replay returned the same requisition. Those temporary resources were deleted afterwards.
Limitations
- Operator routes use one shared secret, not user accounts.
- Live phone calls, full conversational routing and a real ERP weren't verified.
- The public demo isn't a customer deployment.